
yarp (yet another registry parser) is a Python library and collection of tools for examining Windows Registry data during forensic investigations.
The Windows Registry stores configuration information relating to the operating system, installed applications, hardware and user activity. Registry artefacts can provide valuable evidence during incident response and digital forensic examinations.
yarp focuses on accurately parsing Registry hive structures while exposing information that may be overlooked by conventional Registry viewers. It supports damaged and truncated hive files, Registry fragments and the recovery of deleted keys and values.
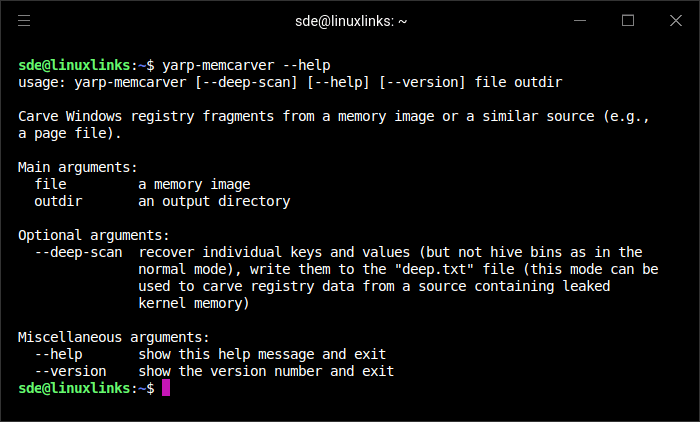
The software also provides functionality for carving Registry data from larger binary sources, making it relevant to investigations involving disk images and memory captures.
yarp supports Registry transaction logs and allows investigators to examine underlying structures rather than relying exclusively on the logical view presented by Windows.
This is free and open source software.
Key Features
- Parses Windows Registry hive files for forensic examination.
- Exposes the underlying structures and fields of Registry data.
- Supports truncated, damaged and fragmented Registry files.
- Recovers deleted Registry keys and values where their data remains available.
- Provides functionality for carving Registry hives and fragments from binary data.
- Supports Registry transaction log analysis.
- Includes utilities for printing, mounting, carving and building timelines from Registry data.
- Offers a Python library for integration with custom forensic tools.
Website: github.com/msuhanov/yarp
Support:
Developer: Maxim Suhanov
License: GNU General Public License v3.0
yarp is written in Python. Learn Python with our recommended free books and free tutorials.
Related Software
| Forensics Memory Tools | |
|---|---|
| MemProcFS | View physical memory as files in a virtual file system |
| pypykatz | Python implementation of Mimikatz |
| PCILeech | Security research and memory acquisition tool |
| Volatility | Advanced memory forensics framework |
| AVML | Acquire Volatile Memory for Linux |
| Volshell | CLI tool for working with memory |
| LeechCore | Physical memory acquisition library |
| EVTXtract | Recovers and reconstructs fragments of EVTX log files |
| mquire | Memory forensics and analysis tool |
| LEMON | Memory acquisition utility |
| yarp | Yet Another Registry Parser |
| emd | Command line memory acquisition tool for Linux systems |
| AutoTimeliner | Extract forensic timeline from volatile memory dump |
Read our verdict in the software roundup.
 LinuxLinks helps you discover the best free and open source software for Linux. Explore our extensive collection of recommended applications, including alternatives to popular proprietary software. We also publish software reviews, Linux tutorials, hardware reviews, free programming books and articles covering the wider open source community. Browse our Linux resources to discover more. Know a useful free and open source Linux application we haven't covered? Suggest a program for inclusion. Has your software been featured on LinuxLinks? Display one of our Featured on LinuxLinks badges on your website or GitHub README. |
Please read our Comment Policy before commenting.