
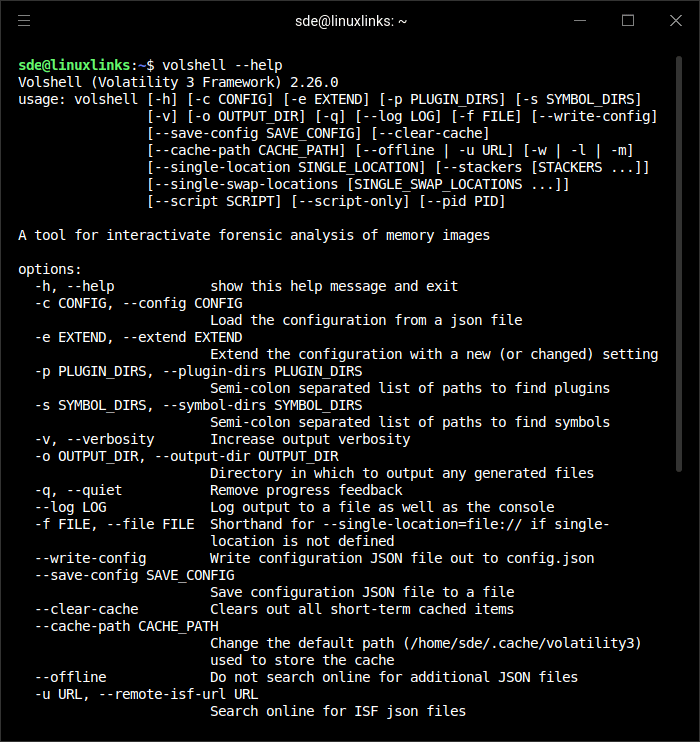
Volshell is a utility to access the volatility framework interactively with a specific memory image. It allows for direct introspection and access to all features of the volatility library from within a command line environment.
Volshell itself is essentially a plugin, but an interactive one. As such, most values are accessed through self although there is also a context object whenever a context must be provided.
The prompt for the tool will indicate the name of the current layer (which can be accessed as self.current_layer from within the tool).
The generic mode is quite limited, won’t have any symbols loaded and therefore won’t be able to display much information. When an operating system is chosen, the appropriate symbols should be loaded and additional functions become available. The mode cannot easily be changed once the tool has started.
This is free and open source software.
Key Features
- List Process.
- Switch into a process’s context.
- Displays types of structure/objects.
- Overlay a type over a given address.
- Walk linked lists.
- Disassemble code at a given address.
Website: volatility3.readthedocs.io/en/latest/volshell.html
Support:
Developer: Volatility Foundation
License: GNU General Public License v2.0
Volshell is written in Python. Learn Python with our recommended free books and free tutorials.
Related Software
| Forensics Memory Tools | |
|---|---|
| MemProcFS | View physical memory as files in a virtual file system |
| pypykatz | Python implementation of Mimikatz |
| PCILeech | Security research and memory acquisition tool |
| Volatility | Advanced memory forensics framework |
| AVML | Acquire Volatile Memory for Linux |
| Volshell | CLI tool for working with memory |
| LeechCore | Physical memory acquisition library |
| EVTXtract | Recovers and reconstructs fragments of EVTX log files |
| mquire | Memory forensics and analysis tool |
| LEMON | Memory acquisition utility |
| yarp | Yet Another Registry Parser |
| emd | Command line memory acquisition tool for Linux systems |
| AutoTimeliner | Extract forensic timeline from volatile memory dump |
Read our verdict in the software roundup.
 Explore our carefully curated directory of recommended free and open source software, covering every major software category. The directory forms part of our extensive collection of articles for Linux enthusiasts. It includes hundreds of detailed reviews, together with free and open source alternatives to proprietary software from companies such as Google, Microsoft, Apple, Adobe, IBM, Cisco, Oracle, and Autodesk. LinuxLinks also covers interesting projects worth exploring, Linux-compatible hardware, free programming books and tutorials, and much more. Know a useful free and open source Linux application that we haven’t covered? Tell us about it using our submission form. |
Please read our Comment Policy before commenting.