
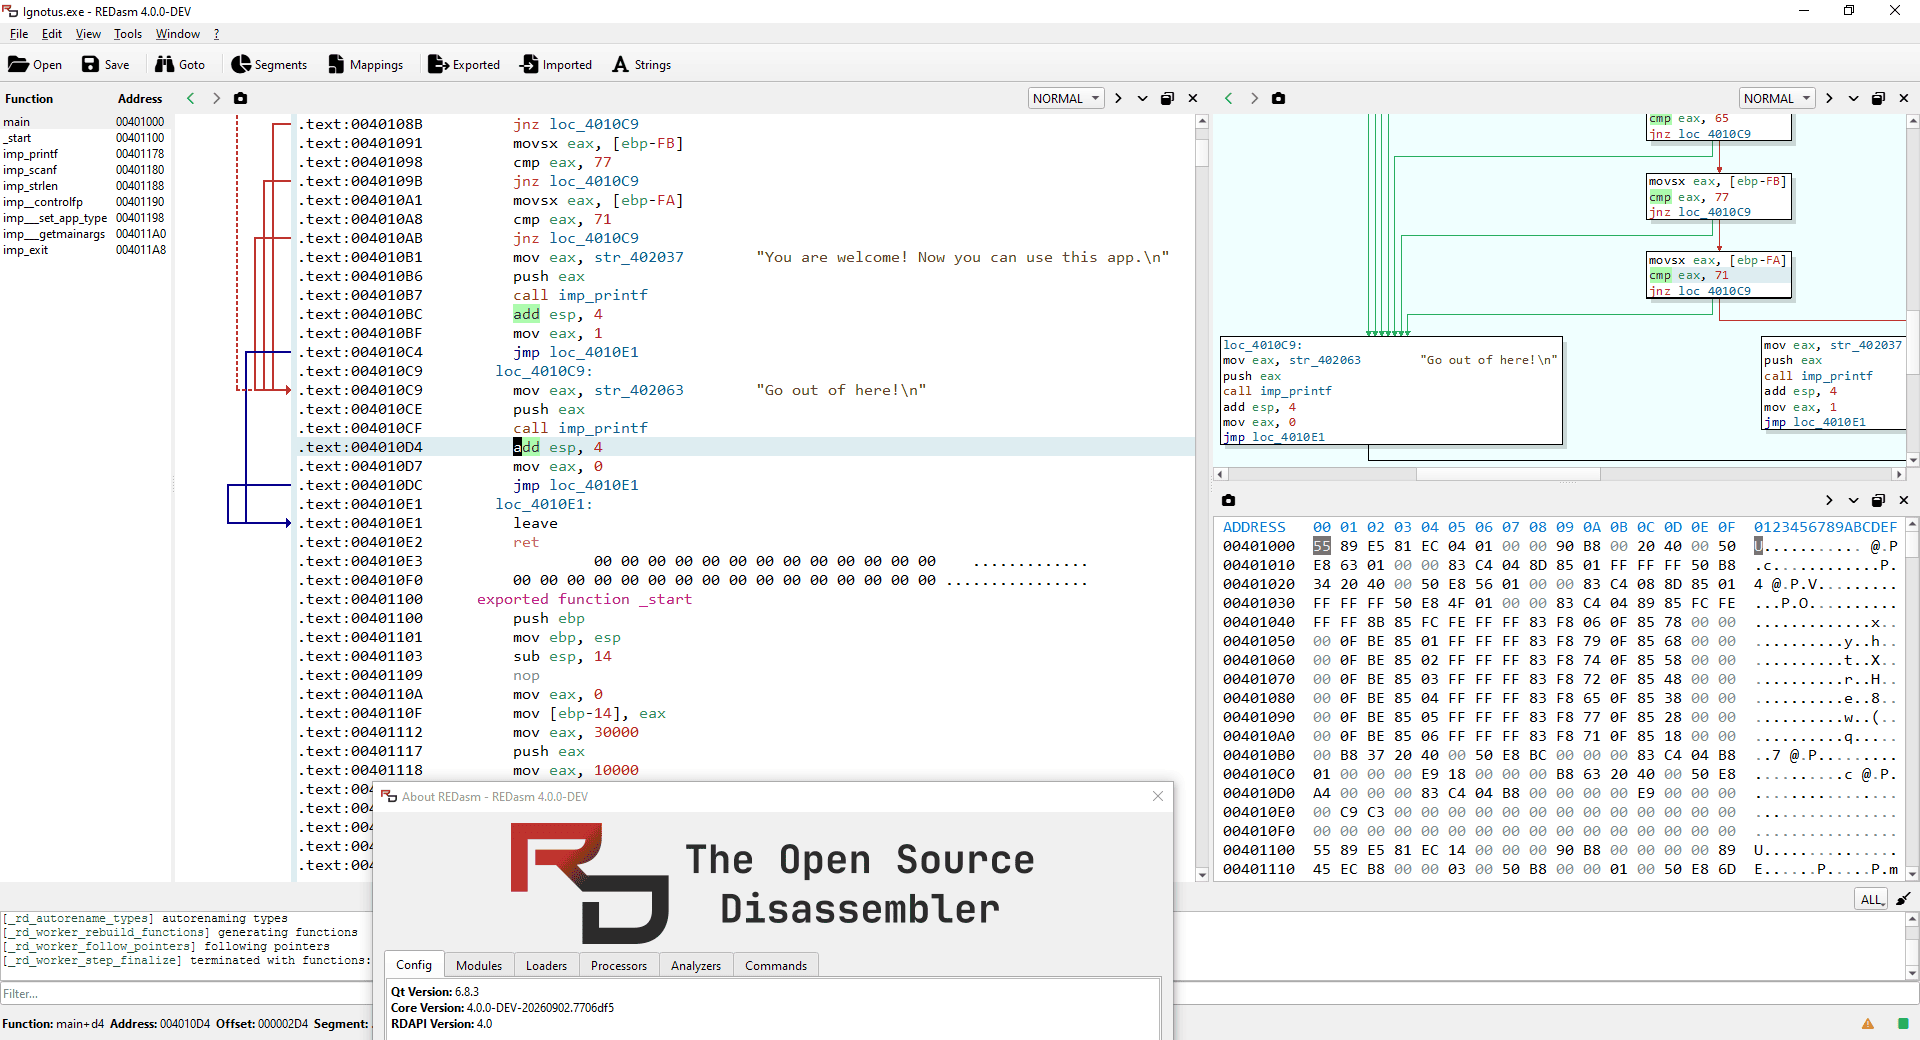
REDasm is a cross-platform disassembler and binary analysis tool for examining compiled programs. It combines a native Qt interface with a separate analysis engine, giving reverse engineers an interactive environment without tying the underlying analysis facilities to the graphical frontend.
The architecture is extensible, with processor support and executable loaders implemented as plugins. REDasm also gives unusual attention to retro and legacy executable formats alongside contemporary binaries, making it relevant for software preservation as well as conventional reverse engineering.
This is free and open source software.
Key Features
- Interactive disassembly listing with renaming, comments and typed data.
- Function-level control flow graphs synchronized with the listing.
- Navigable cross-references for code and data.
- Automatic detection of ASCII, UTF-16 and Latin-1 strings.
- Type system supporting structs, unions, enums and typedefs.
- Integrated hex viewer.
- Panels for segments, imports, exports, symbols, strings and problems.
- Save and restore analysis projects including annotations and renames.
- Patch binaries and export analysis data.
- Architecture-neutral intermediate language for analysis and lifting.
- Support for PE, ELF and several legacy and console formats.
- Processor support including x86, x86-64, ARM, AArch64, MIPS, Z80 and MOS 6502.
- Analyzers for Visual Basic binaries and Microsoft runtime information.
- Light and dark themes.
- Analysis engine can be used independently of the GUI.
Website: github.com/redasm-dev/redasm
Support:
Developer: REDasm developers
License: GNU General Public License v3.0
REDasm is written in C++. Learn C++ with our recommended free books and free tutorials.
Related Software
| Binary Analysis Tools | |
|---|---|
| Ghidra | Software reverse engineering framework |
| Radare2 | Portable reversing framework |
| Cutter | Graphical reverse engineering platform |
| Capstone | Lightweight multi-architecture disassembly framework |
| Detect it Easy | File inspection utility |
| ImHex | Analyze binary data |
| Miasm | Reverse engineering framework for analysing and emulating binaries |
| Reko | General-purpose decompiler for machine-code binaries |
| capa | Command line malware analysis tool |
| binwalk | Search a given binary image for embedded files |
| FLOSS | FLARE Obfuscated String Solver |
| unblob | Extraction suite for working with unknown binary blobs |
| Rizin | UNIX-like reverse engineering framework |
| REDasm | Cross-platform disassembler with an extensible graphical interface |
| Pharos | Framework for automated static analysis of binary programs |
| LIEF | Work with executable and binary formats |
| RetDec | Retargetable machine-code decompiler |
| knife | Static binary triage, disassembly and vulnerability analysis toolkit |
Read our verdict in the software roundup.
 LinuxLinks helps you discover the best free and open source software for Linux. Explore our extensive collection of recommended applications, including alternatives to popular proprietary software. We also publish software reviews, Linux tutorials, hardware reviews, free programming books and articles covering the wider open source community. Browse our Linux resources to discover more. Know a useful free and open source Linux application we haven't covered? Suggest a program for inclusion. Has your software been featured on LinuxLinks? Display one of our Featured on LinuxLinks badges on your website or GitHub README. |
Please read our Comment Policy before commenting.