
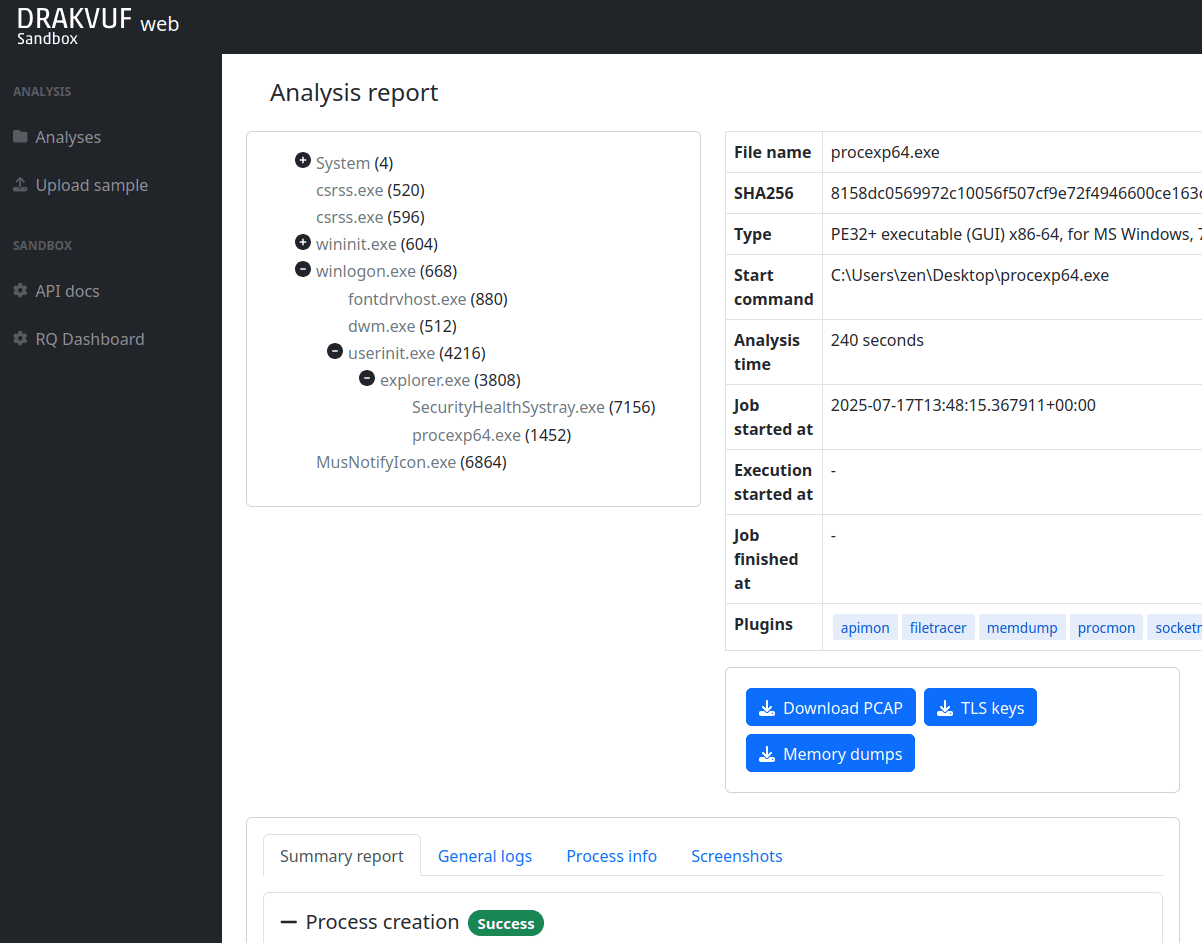
DRAKVUF Sandbox is an automated black-box malware analysis platform built around the DRAKVUF virtual machine introspection engine.
It examines suspicious files in isolated Windows guest systems while keeping the monitoring machinery outside the guest. This agentless approach reduces the instrumentation visible to malware and lets analysts observe behaviour without installing a conventional analysis agent in the target environment. A web interface handles sample submission and presents completed analysis, making the platform useful for malware researchers, incident-response teams and security laboratories that need repeatable behavioural analysis.
This is free and open source software.
Key Features
- Uses DRAKVUF for virtual machine introspection and agentless monitoring of guest activity.
- Provides a web interface for uploading suspicious files and exploring completed analysis results.
- Exposes an API as another primary interface for interacting with the sandbox.
- Includes an installer that guides administrators through the substantial sandbox setup process and supplies recommended defaults.
- Supports Windows guest environments running on a Linux host.
- Built around Xen, with KVM also used by the project for nested-virtualisation development and testing.
- Requires Intel virtualisation support with Extended Page Tables for the intended monitoring architecture.
- Allows experienced administrators to replace or tune infrastructure components rather than treating the deployment as a fixed appliance.
- Stores analyses locally by default and offers optional S3 integration for alternative storage arrangements.
- Separates sandbox execution from the analyst-facing reporting workflow, helping users inspect potentially malicious behaviour from the host side.
- Targets serious malware-analysis deployments rather than lightweight local scanning; upstream warns that maintaining the sandbox can require significant debugging and administration skills.
Website: github.com/CERT-Polska/drakvuf-sandbox
Support:
Developer: CERT Polska – NASK PIB
License: GNU General Public License v2.0
DRAKVUF Sandbox is written in Python and JavaScript. Learn Python with our recommended free books and free tutorials. Learn JavaScript with our recommended free books and free tutorials.
Related Software
| Malware Sandboxes | |
|---|---|
| DRAKVUF Sandbox | Agentless malware analysis using hardware virtualization |
| Cuckoo3 | Automated malware analysis sandbox |
| Nyxelf | Static and dynamic analysis of ELF malware |
| Kunai Sandbox | QEMU-based platform for dynamic malware analysis |
Read our verdict in the software roundup.
 Explore our carefully curated directory of recommended free and open source software, covering every major software category. The directory forms part of our extensive collection of articles for Linux enthusiasts. It includes hundreds of detailed reviews, together with free and open source alternatives to proprietary software from companies such as Google, Microsoft, Apple, Adobe, IBM, Cisco, Oracle, and Autodesk. LinuxLinks also covers interesting projects worth exploring, Linux-compatible hardware, free programming books and tutorials, and much more. Know a useful free and open source Linux application that we haven’t covered? Tell us about it using our submission form. |
Please read our Comment Policy before commenting.