
The Sleuth Kit (TSK) is a collection of command-line utilities and libraries for examining disk images, storage volumes and file systems during digital forensic investigations. It provides low-level access to file system structures, allowing investigators to inspect allocated and deleted files, recover data, examine metadata and reconstruct activity without relying on the operating system that originally used the storage device.
Its tools operate at different layers of a storage system, from identifying partitions to interpreting file system metadata and extracting individual data blocks. Investigators can combine these utilities to examine evidence from acquired disk images or analyse supported file systems directly. The underlying library is also used by other forensic applications, including Autopsy, to provide file system analysis capabilities through higher-level interfaces.
This is free and open source software.
Key Features
- Analyse raw disk images, Expert Witness images and supported AFF containers.
- Support for NTFS, FAT, exFAT, Ext2, Ext3, Ext4, HFS, ISO 9660, UFS and YAFFS2 file systems.
- Examine partition tables and volume layouts using tools such as mmls.
- List allocated and deleted file names with fls.
- Extract file contents directly from metadata addresses using icat.
- Inspect file metadata and file system structures using istat and fsstat.
- Recover unallocated data blocks for further examination with blkls.
- Examine individual storage blocks using blkcat and blkstat.
- Identify the metadata entries associated with particular files and data units.
- Examine NTFS attributes, including alternate data streams.
- Generate body files and file activity timelines using fls and mactime.
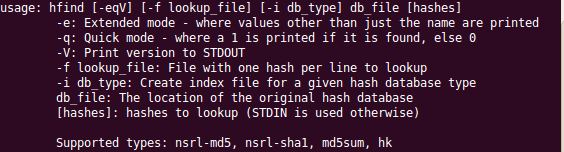
- Index hash databases with hfind to accelerate known-file identification.
- Calculate file hashes and compare evidence against reference hash collections.
- Provide reusable libraries for integration with other forensic applications.
- Cross-platform support – runs on Linux, macOS, and Windows.
Website: www.sleuthkit.org
Support:
Developer: Brian Carrier
License: IBM Public License v1.0, Common Public License v1.0, GNU General Public License v2.0
TSK is written in C, C++, and Java. Learn C with our recommended free books and free tutorials. Learn C++ with our recommended free books and free tutorials. Learn Java with our recommended free books and free tutorials.
Related Software
| Digital Forensics Tools | |
|---|---|
| GRR Rapid Response | Remote live forensics for incident response |
| Radare2 | Portable reversing framework |
| The Sleuth Kit | Collection of tools for forensic analysis |
| MemProcFS | View physical memory as files in a virtual file system |
| Autopsy Forensic Browser | Graphical interface to SleuthKit |
| iaito | Official graphical interface for radare2 |
| Chainsaw | Fast forensic triage and threat hunting tool for Windows artefacts |
| Velociraptor | Endpoint visibility and collection tool |
| Timesketch | Collaborative forensic timeline analysis |
| Plaso | Python-based digital forensics framework |
| Volatility | Advanced memory forensics framework |
| UAC | Collect forensic artefacts from Linux and other Unix-like systems |
| IPED | Process, index and analyse large collections of digital evidence |
| guymager | Forensic imaging tool based on Qt |
| Dissect | Access and query evidence across disk images and file systems |
| dcfldd | Enhanced version of dd for forensics and security |
| rdd | Forensic copy program |
| Jomon | Network forensics and passive sniffer |
| Mozilla InvestiGator | Real-time digital forensics and investigation platform |
Read our verdict in the software roundup.
| Data Recovery Tools | |
|---|---|
| ddrescue | GNU data recovery tool |
| The Sleuth Kit | Analyze disk images and recover files |
| SystemRescue | System rescue disk |
| TestDisk | Partition scanner and disk recovery tool |
| Relax-and-Recover | Linux Disaster Recovery |
| RecoverPy | Terminal-based data recovery tool |
| Mondo Rescue | Tool for configuring and maintaining network machines |
| PhotoRec | Digital Picture and File Recovery |
| Rescuezilla | Complete disaster recovery solution |
| OpenSuperClone | Powerful data recovery utility |
| Mariposa Rescue Disk | Comes with a lot of applications that serve to rescue your system |
| safecopy | Copy utility ignoring errors |
| Redo Rescue | Backup and recovery solution |
| Foremost | Recover files based on their headers, footers, and data structures |
| DDRescue-GUI | Frontend for ddrescue |
| Scalpel | Data carving tool |
| ext4magic | Recover deleted or overwritten files |
| RevLix | Developed to recover deleted files on Linux systems |
Read our verdict in the software roundup.
 LinuxLinks helps you discover the best free and open source software for Linux. Explore our extensive collection of recommended applications, including alternatives to popular proprietary software. We also publish software reviews, Linux tutorials, hardware reviews, free programming books and articles covering the wider open source community. Browse our Linux resources to discover more. Know a useful free and open source Linux application we haven't covered? Suggest a program for inclusion. Has your software been featured on LinuxLinks? Display one of our Featured on LinuxLinks badges on your website or GitHub README. |
Please read our Comment Policy before commenting.