
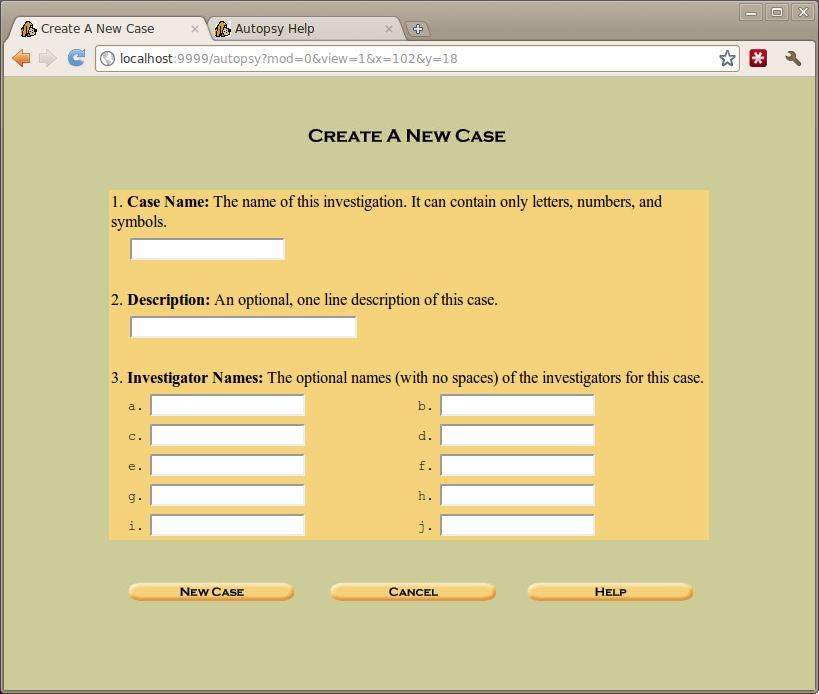
The Autopsy Forensic Browser is a graphical interface to the command line digital investigation tools in The Sleuth Kit. The two together enable users to investigate volumes and file systems including NTFS, FAT, UFS1/2, and Ext2/3 in a ‘File Manager’ style interface and perform key word searches.
TSK and Autopsy will show you the files, data units, and metadata of NTFS, FAT, EXTxFS, and UFS file system images in a read-only environment. Autopsy allows you to search for specific types of evidence based on keywords, MAC times, hash values, and file types.
Autopsy is HTML-based and uses a client-server model. The Autopsy server runs on many systems and the client can be any platform with an HTML browser. This enables one to create a flexible environment with a central Autopsy server and several remote clients. For incident response scenarios, a CD with The Sleuth Kit and Autopsy can be created to allow the responder read-only remote access to a live suspect system from an HTML-browser on a trusted system. Refer to the README-live.txt file for more details.
Autopsy will not modify the original images and the integrity of the images can be verified in Autopsy using MD5 values.
Key Features
- Analyze the files and directories, including the names of deleted files and files with Unicode-based names.
- The contents of files can be viewed in raw, hex, or the ASCII strings can be extracted.
- Lookup unknown files in a hash database to quickly identify it as good or bad.
- Sort the files based on their internal signatures to identify files of a known type. Autopsy can also extract only graphic images (including thumbnails). The extension of the file will also be compared to the file type to identify files that may have had their extension changed to hide them.
- Create timelines that contain entries for the Modified, Access, and Change (MAC) times of both allocated and unallocated files.
- Keyword searches of the file system image can be performed using ASCII strings and grep regular expressions.
- Meta Data structures contain the details about files and directories. Autopsy allows you to view the details of any meta data structure in the file system.
- View the contents of any data unit in a variety of formats including ASCII, hexdump, and strings.
- File system details can be viewed, including on-disk layout and times of activity.
- Supports raw, Expert Witness, and AFF file formats.
Website: www.sleuthkit.org/autopsy
Support: Wiki
Developer: Brian Carrier
License: GNU General Public License v2.0
Autopsy is written in C and Perl. Learn C with our recommended free books and free tutorials. Learn Perl with our recommended free books and free tutorials.
Related Software
| Digital Forensics Tools | |
|---|---|
| GRR Rapid Response | Remote live forensics for incident response |
| Radare2 | Portable reversing framework |
| The Sleuth Kit | Collection of tools for forensic analysis |
| MemProcFS | View physical memory as files in a virtual file system |
| Autopsy Forensic Browser | Graphical interface to SleuthKit |
| iaito | Official graphical interface for radare2 |
| Chainsaw | Fast forensic triage and threat hunting tool for Windows artefacts |
| Velociraptor | Endpoint visibility and collection tool |
| Timesketch | Collaborative forensic timeline analysis |
| Plaso | Python-based digital forensics framework |
| Volatility | Advanced memory forensics framework |
| UAC | Collect forensic artefacts from Linux and other Unix-like systems |
| IPED | Process, index and analyse large collections of digital evidence |
| guymager | Forensic imaging tool based on Qt |
| Dissect | Access and query evidence across disk images and file systems |
| dcfldd | Enhanced version of dd for forensics and security |
| rdd | Forensic copy program |
| Jomon | Network forensics and passive sniffer |
| Mozilla InvestiGator | Real-time digital forensics and investigation platform |
Read our verdict in the software roundup.
 LinuxLinks helps you discover the best free and open source software for Linux. Explore our extensive collection of recommended applications, including alternatives to popular proprietary software. We also publish software reviews, Linux tutorials, hardware reviews, free programming books and articles covering the wider open source community. Browse our Linux resources to discover more. Know a useful free and open source Linux application we haven't covered? Suggest a program for inclusion. Has your software been featured on LinuxLinks? Display one of our Featured on LinuxLinks badges on your website or GitHub README. |
Please read our Comment Policy before commenting.