
MIG is Mozilla’s platform for investigative surgery of remote endpoints.
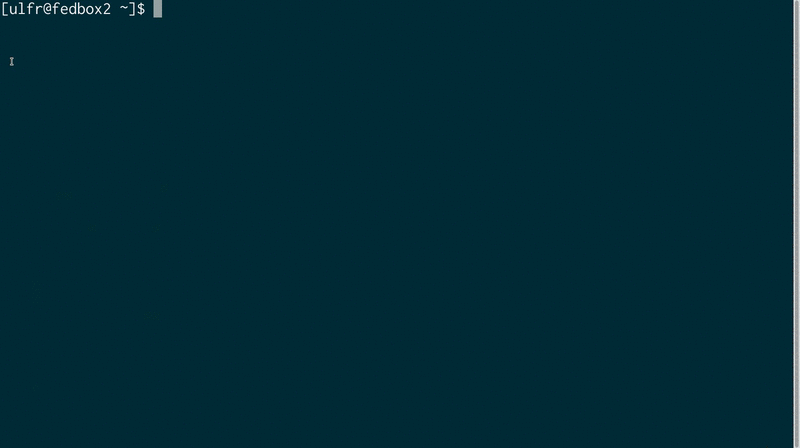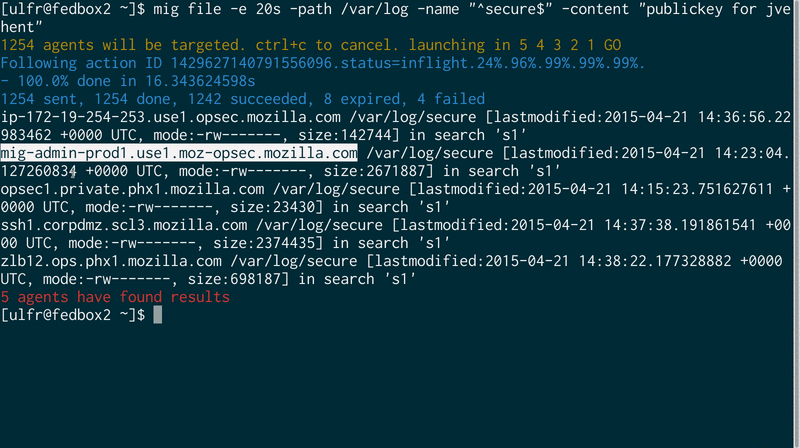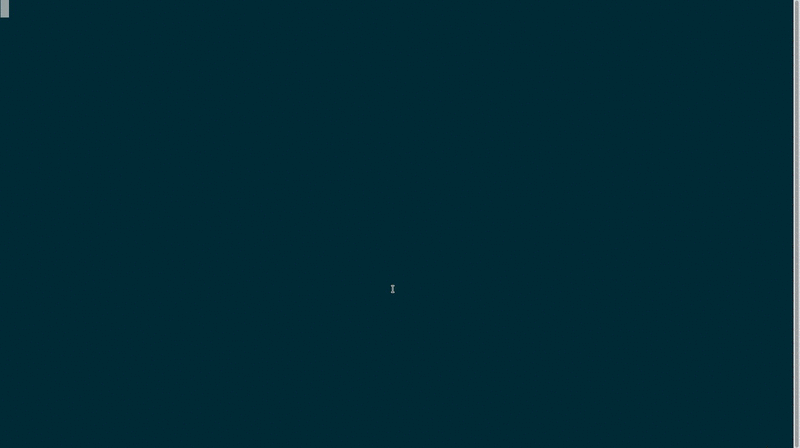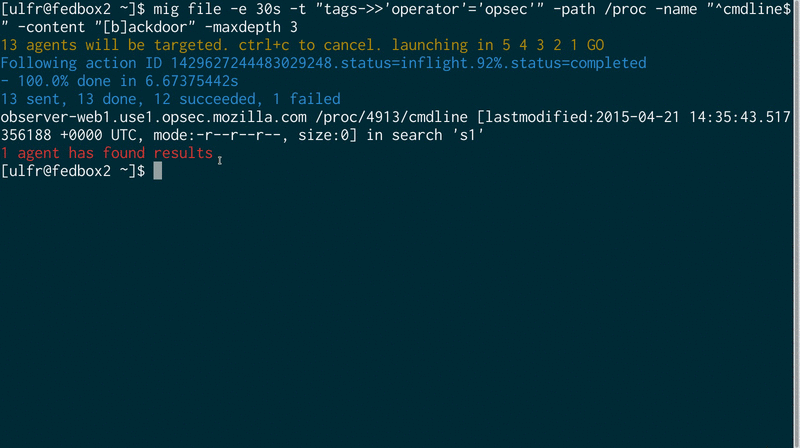
It enables investigators to obtain information from large numbers of systems in parallel, thus accelerating investigation of incidents and day-to-day operations security.
MIG is composed of agents installed on all systems of an infrastructure that are be queried in real-time to investigate the file-systems, network state, memory or configuration of endpoints. MIG agents are designed to be lightweight, secure, and easy to deploy
It’s an army of Sherlock Holmes, ready to interrogate your infrastructure within seconds.
MIG uses a REST API that receives signed JSON messages distributed to agents via RabbitMQ and stored in a Postgres database.
Key Features
- File inspection.
- Network inspection.
- Memory inspection
- Vuln management.
- System auditing.
- Designed to be fast, and asynchronous.
- It uses AMQP to distribute actions to endpoints, and relies on Go channels to prevent components from blocking.
- Running actions and commands are stored in a Postgresql database and on disk cache, such that the reliability of the platform doesn’t depend on long-running processes.
- Massively distributed means fast.
- Simple to deploy
- Secured using OpenPGP.
- Respectful of privacy by never retrieving raw data from endpoints.
- Cross-platform support.
Website: github.com/mozilla/mig
Support:
Developer: Mozilla Foundation
License: Mozilla Public License 2.0
MIG is written in Go. Learn Go with our recommended free books and free tutorials.
Related Software
| Digital Forensics Tools | |
|---|---|
| GRR Rapid Response | Remote live forensics for incident response |
| Radare2 | Portable reversing framework |
| The Sleuth Kit | Collection of tools for forensic analysis |
| MemProcFS | View physical memory as files in a virtual file system |
| Autopsy Forensic Browser | Graphical interface to SleuthKit |
| iaito | Official graphical interface for radare2 |
| Chainsaw | Fast forensic triage and threat hunting tool for Windows artefacts |
| Velociraptor | Endpoint visibility and collection tool |
| Timesketch | Collaborative forensic timeline analysis |
| Plaso | Python-based digital forensics framework |
| Volatility | Advanced memory forensics framework |
| UAC | Collect forensic artefacts from Linux and other Unix-like systems |
| IPED | Process, index and analyse large collections of digital evidence |
| guymager | Forensic imaging tool based on Qt |
| Dissect | Access and query evidence across disk images and file systems |
| dcfldd | Enhanced version of dd for forensics and security |
| rdd | Forensic copy program |
| Jomon | Network forensics and passive sniffer |
| Mozilla InvestiGator | Real-time digital forensics and investigation platform |
Read our verdict in the software roundup.
 LinuxLinks helps you discover the best free and open source software for Linux. Explore our extensive collection of recommended applications, including alternatives to popular proprietary software. We also publish software reviews, Linux tutorials, hardware reviews, free programming books and articles covering the wider open source community. Browse our Linux resources to discover more. Know a useful free and open source Linux application we haven't covered? Suggest a program for inclusion. Has your software been featured on LinuxLinks? Display one of our Featured on LinuxLinks badges on your website or GitHub README. |
Please read our Comment Policy before commenting.