
rdd is a forensic copy program developed at and used by the Netherlands Forensic Institute (NFI).
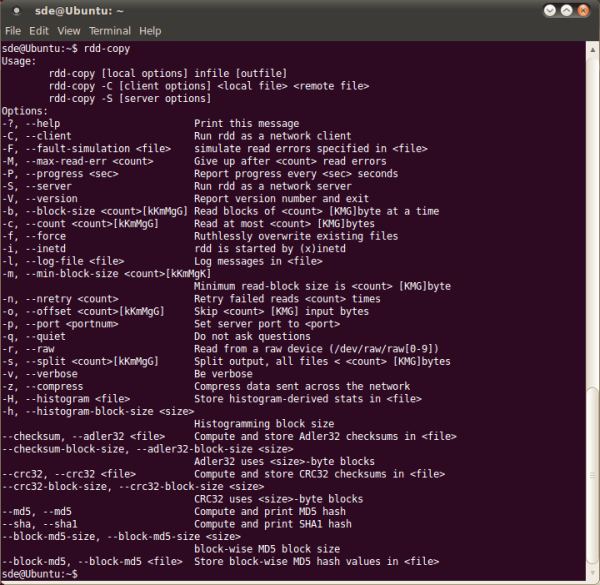
Specifically, rdd is a file and device copying utility that includes features that are useful in a forensic environment. In particular, rdd can compute cryptographic hashes over the data it copies, which is an important property in a forensic operating environment. The software is also robust with respect to read errors, and can copy data across a network.
rdd can be run in local mode, in client mode, and in server mode.
Key Features
- Checksumming (Adler32 and CRC32) – computes an MD5 or a SHA1 hash value over the input bytes and the zero bytes it substitutes for blocks it cannot read.
- Access the device using the raw device.
- Designed to handle unfriendly source media.
Website: sourceforge.net/projects/rdd
Support:
Developer: Raoul A.F. Bhoedjang and contributors
License: Open Source
rdd is written in C. Learn C with our recommended free books and free tutorials.
Related Software
| Digital Forensics Tools | |
|---|---|
| GRR Rapid Response | Remote live forensics for incident response |
| Radare2 | Portable reversing framework |
| The Sleuth Kit | Collection of tools for forensic analysis |
| MemProcFS | View physical memory as files in a virtual file system |
| Autopsy Forensic Browser | Graphical interface to SleuthKit |
| iaito | Official graphical interface for radare2 |
| Chainsaw | Fast forensic triage and threat hunting tool for Windows artefacts |
| Velociraptor | Endpoint visibility and collection tool |
| Timesketch | Collaborative forensic timeline analysis |
| Plaso | Python-based digital forensics framework |
| Volatility | Advanced memory forensics framework |
| UAC | Collect forensic artefacts from Linux and other Unix-like systems |
| IPED | Process, index and analyse large collections of digital evidence |
| guymager | Forensic imaging tool based on Qt |
| Dissect | Access and query evidence across disk images and file systems |
| dcfldd | Enhanced version of dd for forensics and security |
| rdd | Forensic copy program |
| Jomon | Network forensics and passive sniffer |
| Mozilla InvestiGator | Real-time digital forensics and investigation platform |
Read our verdict in the software roundup.
 LinuxLinks helps you discover the best free and open source software for Linux. Explore our extensive collection of recommended applications, including alternatives to popular proprietary software. We also publish software reviews, Linux tutorials, hardware reviews, free programming books and articles covering the wider open source community. Browse our Linux resources to discover more. Know a useful free and open source Linux application we haven't covered? Suggest a program for inclusion. Has your software been featured on LinuxLinks? Display one of our Featured on LinuxLinks badges on your website or GitHub README. |
Please read our Comment Policy before commenting.