
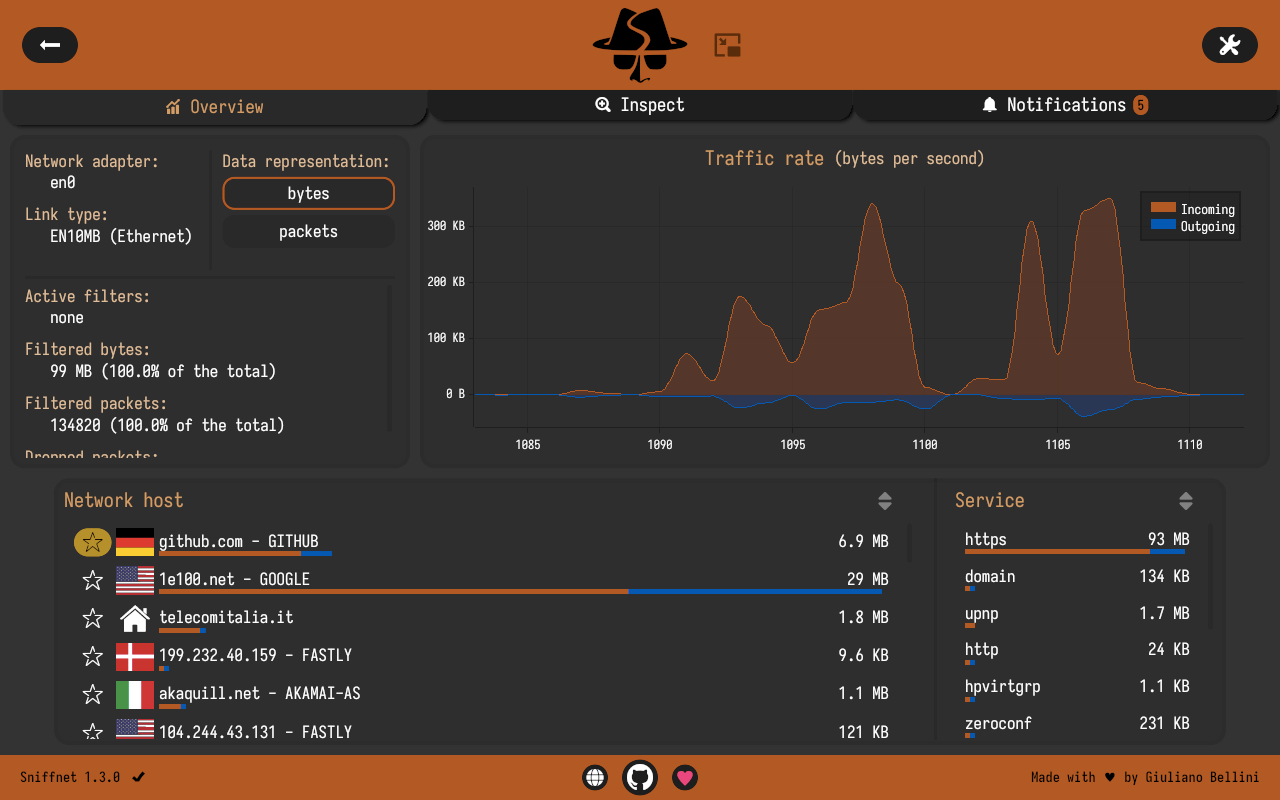
Sniffnet is a network monitoring tool to help you easily keep track of your internet traffic.
Whether you want to gather statistics, or you need to inspect more in depth what’s going on in your network, this app will get you covered.
Sniffnet is a technical tool, but at the same time it strongly focuses on the overall user experience: most of the network analyzers out there are cumbersome to use, while one of Sniffnet’s cornerstones is to be usable with ease by everyone.
This is free and open source software.
Features include:
- Choose a network adapter of your PC to inspect.
- Select a set of filters to apply to the observed traffic.
- View overall statistics about your Internet traffic.
- View real-time charts about traffic intensity.
- Keep an eye on your network even when the application is minimized.
- Export comprehensive capture reports as PCAP files.
- Identify 6000+ upper layer services, protocols, trojans, and worms.
- Find out domain name and ASN of the hosts you are exchanging traffic with.
- Identify connections in your local network.
- Discover the geographical location of the remote hosts.
- Save your favorite network hosts.
- Inspect each of your network connections in real time.
- Set custom notifications to inform you when defined network events occur.
- Choose the style that fits you the most, including custom themes support.
Website: sniffnet.app
Support: GitHub Code Repository
Developer: Giuliano Bellini and contributors
License: Apache License 2.0 or MIT License
Sniffnet is written in Rust. Learn Rust with our recommended free books and free tutorials
Related Software
| Network Analyzers | |
|---|---|
| Wireshark | Network protocol analyzer with a rich and powerful feature set |
| Sniffnet | Visualise live network traffic with a friendly interface |
| Kismet | Wireless network and device detector, sniffer, wardriving tool |
| Ettercap | Comprehensive suite for man in the middle attacks |
| IPTraf-ng | Feature-laden network statistic monitoring tool |
| Zeek | Network security monitoring with deep traffic insight |
| netsniff-ng | Swiss army knife for daily Linux network plumbing |
| Kyanos | Networking analysis tool using eBPF |
| Arkime | Indexes full packet captures for rapid, large-scale traffic investigation |
| EtherApe | Graphical network monitor |
| darkstat | Captures network traffic, calculates usage statistics, and serves reports |
| justniffer | Network TCP packet sniffer with reliable TCP flow rebuilding |
| tcpflow | TCP/IP packet demultiplexer |
| tcpdump | Powerful and hugely respected command-line packet analyzer |
| sniffglue | Packet sniffer written in Rust |
| sniffer | Alternative network traffic sniffer |
| RustNet | Terminal monitor for connections and bandwidth |
| Malcolm | Traffic analysis suite for capture, hunting and forensics |
| dsniff | Collection of tools for network auditing and penetration testing |
| ngrep | grep applied to the network layer |
| Network Monitor | Rreal-time network connection monitoring tool |
| sniffit | CORBA based sniffer system with ncurses interactive mode |
| Jomon | Network forensics and sniffer tool |
Read our verdict in the software roundup.
 Explore our carefully curated directory of recommended free and open source software, covering every major software category. The directory forms part of our extensive collection of articles for Linux enthusiasts. It includes hundreds of detailed reviews, together with free and open source alternatives to proprietary software from companies such as Google, Microsoft, Apple, Adobe, IBM, Cisco, Oracle, and Autodesk. LinuxLinks also covers interesting projects worth exploring, Linux-compatible hardware, free programming books and tutorials, and much more. Know a useful free and open source Linux application that we haven’t covered? Tell us about it using our submission form. |
Please read our Comment Policy before commenting.
Thanks I didn’t know about this 🙂
By the way the GitHub link is wrong, here’s the right one
Thanks, GitHub link now fixed.