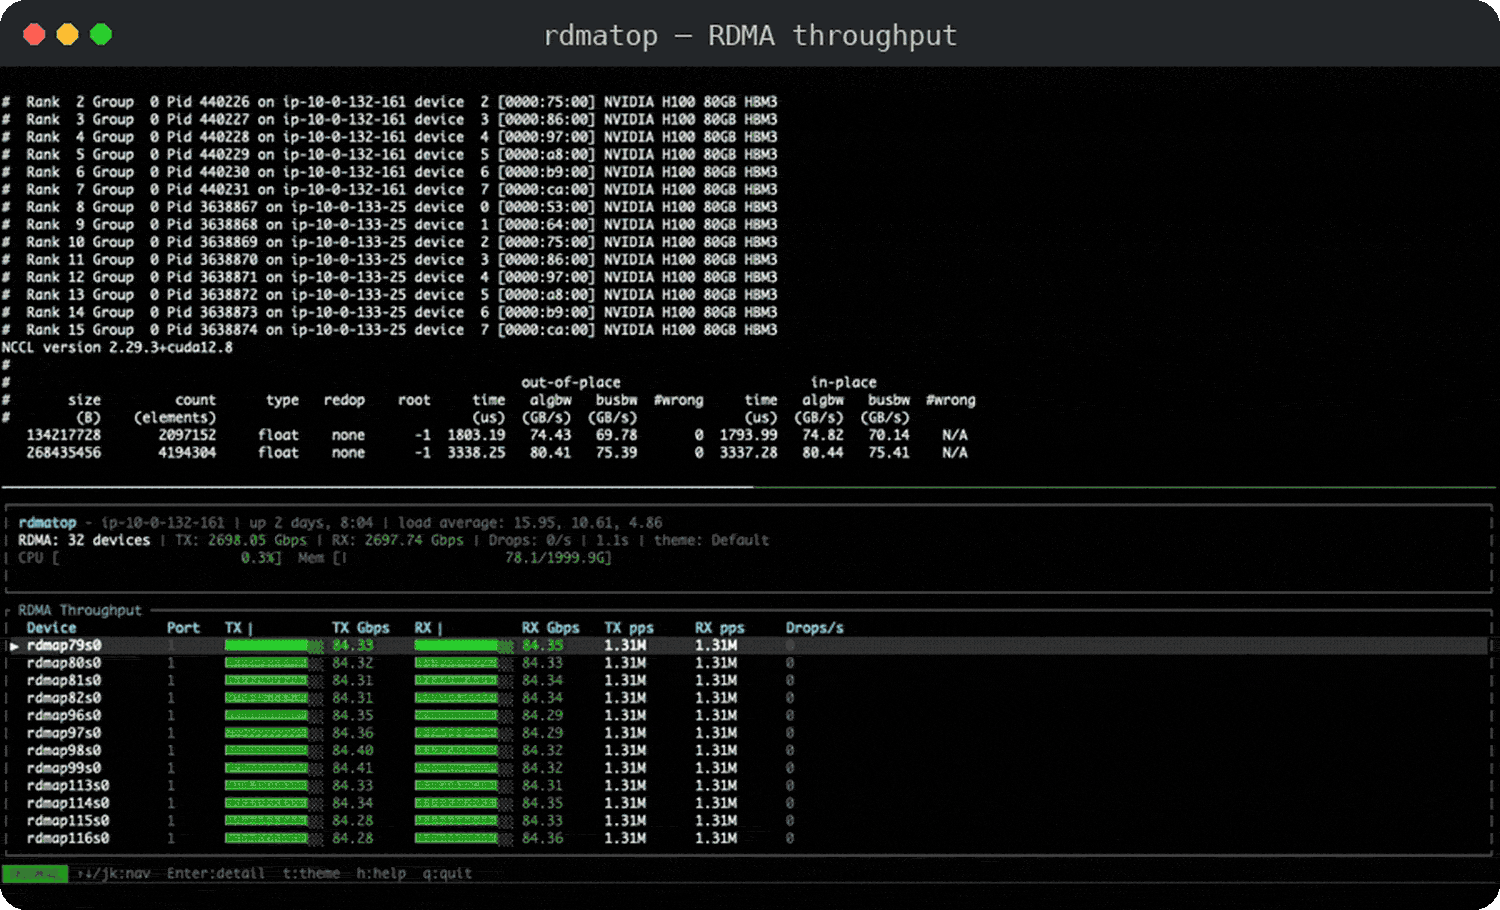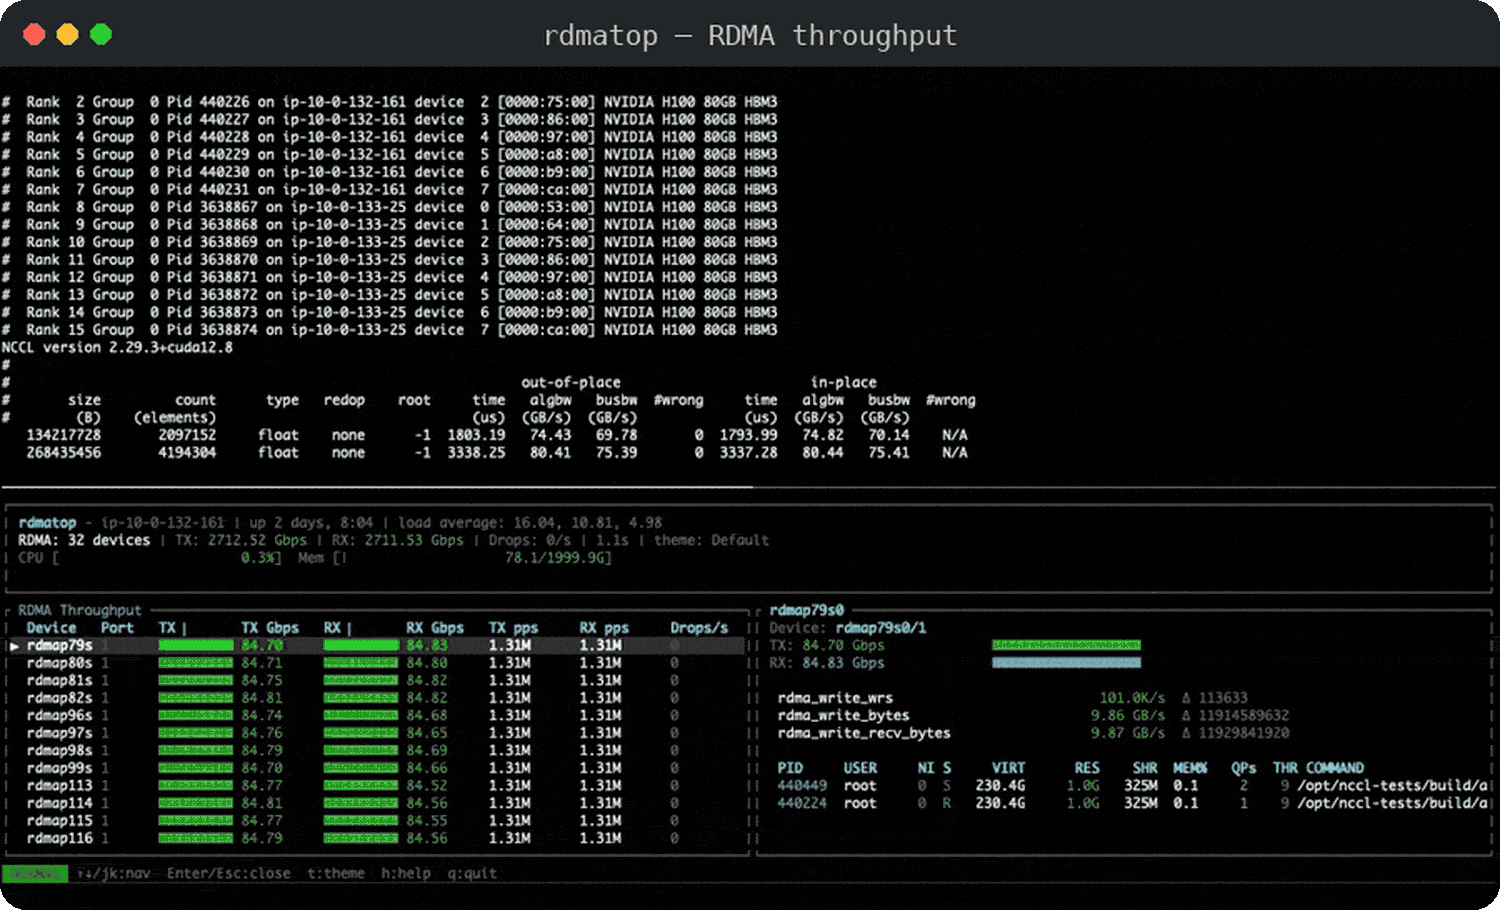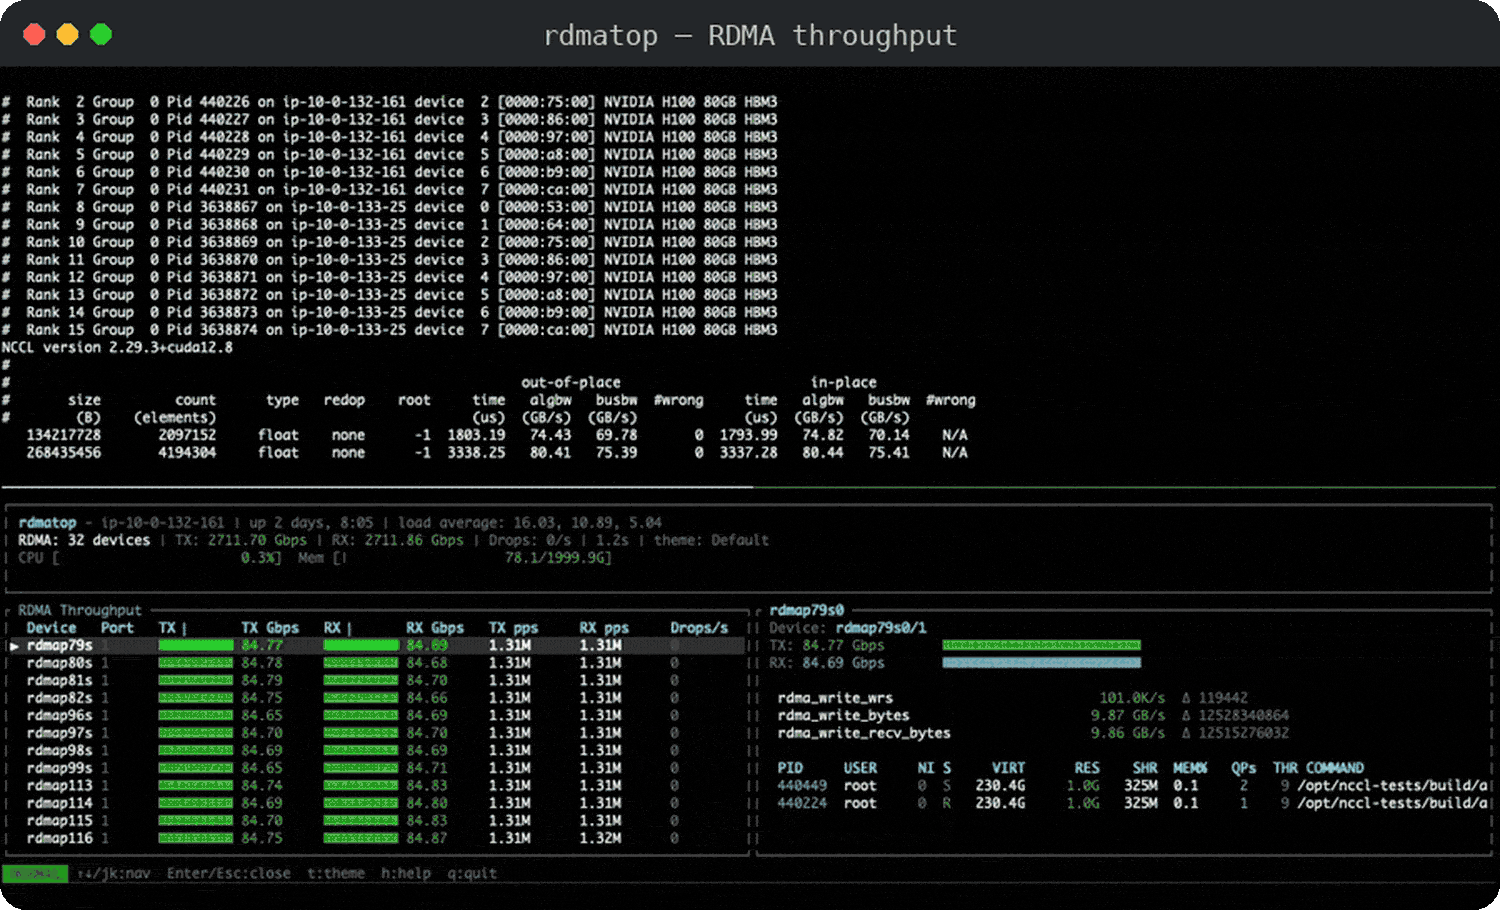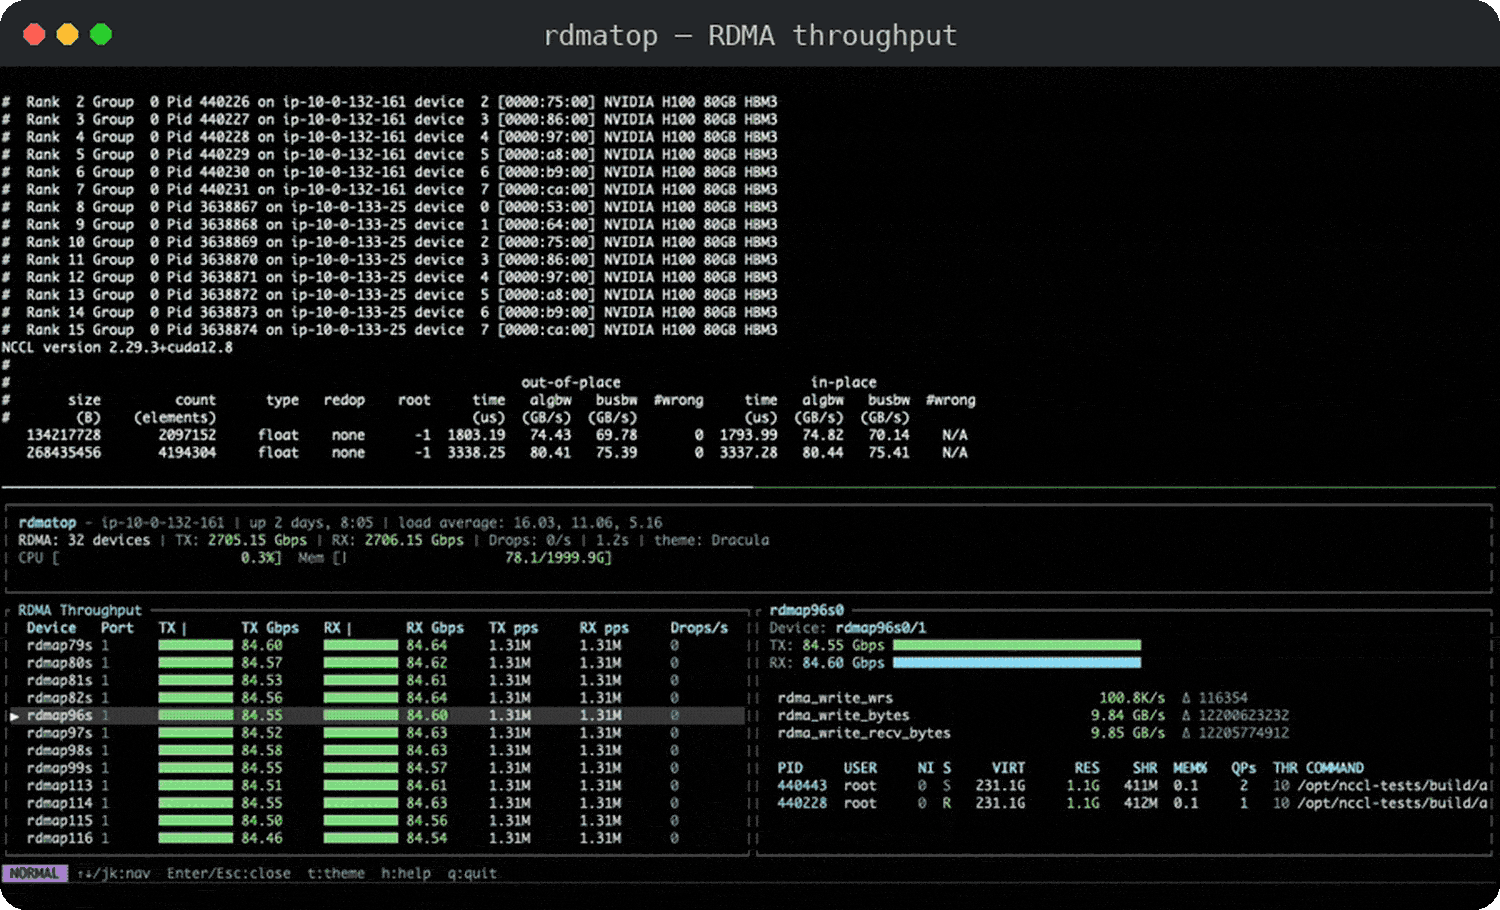
rdmatop is a Linux terminal user interface for monitoring Remote Direct Memory Access (RDMA) network activity in real time.
It provides an htop-style view of RDMA devices without tying monitoring to a particular NIC vendor. The program reads the kernel’s RDMA netlink interface, the same underlying interface used by rdma statistic, and combines hardware counters with process information. This makes it useful for diagnosing communication bottlenecks on GPU clusters and other systems using InfiniBand, RoCE, AWS EFA or other Linux RDMA providers.
This is free and open source software.
Key Features
- Displays transmit and receive throughput for individual RDMA devices and ports.
- Reports traffic rates in Gbps and packets per second.
- Shows packet drops, retransmissions, RDMA reads and RDMA writes.
- Maps RDMA queue pairs to the processes that own them using netlink and /proc data.
- Surfaces health events to help identify problematic devices and links.
- Enumerates RDMA devices through RDMA_NLDEV_CMD_GET rather than vendor-specific monitoring interfaces.
- Retrieves hardware statistics through RDMA_NLDEV_CMD_STAT_GET.
- Calculates throughput from successive counter snapshots and elapsed time.
- Records device throughput and packet-rate counters to Chrome JSON traces for analysis with Perfetto.
- Supports RDMA environments built around NVIDIA/Mellanox ConnectX, AWS EFA and other providers exposed through Linux RDMA netlink.
- Can be used alongside communication workloads including NCCL, NVSHMEM, UCX, NIXL and IB Perftest.
- Includes process-level visibility that helps associate fabric traffic with running workloads.
Website: github.com/uccl-project/rdmatop
Support:
Developer: Chang-Ning Tsai and the UCCL Team
License: Apache License 2.0
rdmatop is written in Rust. Learn Rust with our recommended free books and free tutorials.
Related Software
| Network Analyzers | |
|---|---|
| Wireshark | Network protocol analyzer with a rich and powerful feature set |
| Sniffnet | Visualise live network traffic with a friendly interface |
| Kismet | Wireless network and device detector, sniffer, wardriving tool |
| Ettercap | Comprehensive suite for man in the middle attacks |
| IPTraf-ng | Feature-laden network statistic monitoring tool |
| Zeek | Network security monitoring with deep traffic insight |
| netsniff-ng | Swiss army knife for daily Linux network plumbing |
| Kyanos | Networking analysis tool using eBPF |
| Arkime | Indexes full packet captures for rapid, large-scale traffic investigation |
| EtherApe | Graphical network monitor |
| darkstat | Captures network traffic, calculates usage statistics, and serves reports |
| justniffer | Network TCP packet sniffer with reliable TCP flow rebuilding |
| tcpflow | TCP/IP packet demultiplexer |
| tcpdump | Powerful and hugely respected command-line packet analyzer |
| sniffglue | Packet sniffer written in Rust |
| sniffer | Alternative network traffic sniffer |
| RustNet | Terminal monitor for connections and bandwidth |
| Malcolm | Traffic analysis suite for capture, hunting and forensics |
| dsniff | Collection of tools for network auditing and penetration testing |
| ngrep | grep applied to the network layer |
| Network Monitor | Rreal-time network connection monitoring tool |
| sniffit | CORBA based sniffer system with ncurses interactive mode |
| Jomon | Network forensics and sniffer tool |
Read our verdict in the software roundup.
 Explore our comprehensive directory of recommended free and open source software. Our carefully curated collection spans every major software category. This directory is part of our ongoing series of informative articles for Linux enthusiasts. It features hundreds of detailed reviews, along with open source alternatives to proprietary solutions from major corporations such as Google, Microsoft, Apple, Adobe, IBM, Cisco, Oracle, and Autodesk. You’ll also find interesting projects to try, hardware coverage, free programming books and tutorials, and much more. Discovered a useful open source Linux program that we haven’t covered yet? Let us know by completing this form. |
Please read our Comment Policy before commenting.