
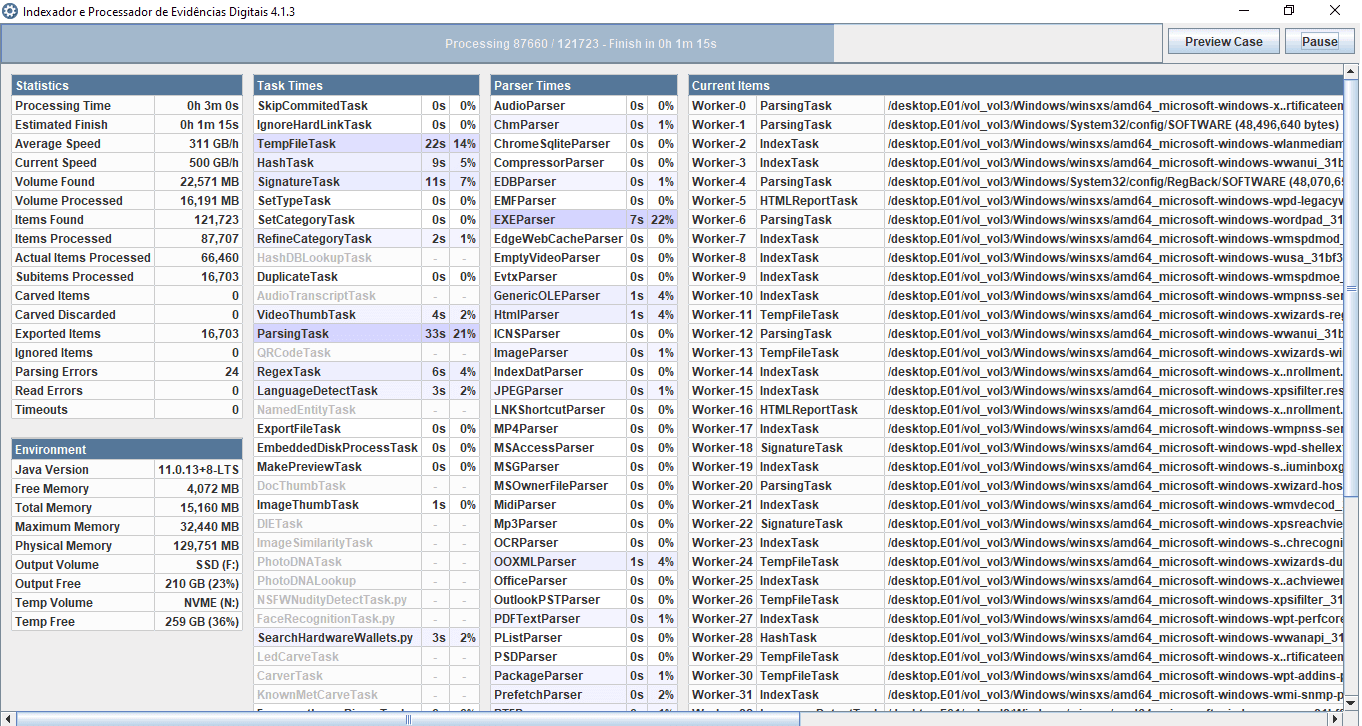
IPED (Digital Evidence Processor and Indexer) is a Java-based digital forensics platform for processing and analysing large collections of digital evidence.
It combines command-line case processing with an integrated analysis interface, allowing investigators to ingest evidence, create searchable indexes and examine files, metadata and relationships within a case. The software was originally developed by digital forensic specialists from the Brazilian Federal Police and remains focused on efficient processing and handling substantial evidence sets.
IPED supports Linux and Windows and can create portable cases that can subsequently be examined without installing the full processing environment.
This is free and open source software.
Key Features
- Processes RAW/DD, E01, EX01, VHD, VHDX, VMDK, AFF, ISO, AD1 and UFDR evidence.
- Indexes file contents and metadata for fast searching.
- Supports multiple cryptographic hashes, reference hash sets and hash-based deduplication.
- Recursively expands archives, containers and embedded forensic disk images.
- Includes a data-carving engine supporting many file formats.
- Performs file signature analysis, optical character recognition and encryption detection.
- Provides image and video galleries and geographic visualization.
- Supports similar document, image and face searches.
- Offers a unified timeline view with event filtering.
- Provides regular-expression searches with optional validation scripts.
- Includes parsers for browser history, messaging applications and other structured evidence.
- Supports JavaScript and Python extensions and integration with external command-line tools.
- Provides bookmarks, HTML and CSV reports, portable cases and a web API.
Website: github.com/sepinf-inc/IPED
Support:
Developer: Brazilian Federal Police digital forensic experts
License: GNU General Public License v3.0
IPED is written in Java. Learn Java with our recommended free books and free tutorials.
Related Software
| Network Analyzers | |
|---|---|
| Wireshark | Network protocol analyzer with a rich and powerful feature set |
| Sniffnet | Visualise live network traffic with a friendly interface |
| Kismet | Wireless network and device detector, sniffer, wardriving tool |
| Ettercap | Comprehensive suite for man in the middle attacks |
| IPTraf-ng | Feature-laden network statistic monitoring tool |
| Zeek | Network security monitoring with deep traffic insight |
| netsniff-ng | Swiss army knife for daily Linux network plumbing |
| Kyanos | Networking analysis tool using eBPF |
| Arkime | Indexes full packet captures for rapid, large-scale traffic investigation |
| EtherApe | Graphical network monitor |
| darkstat | Captures network traffic, calculates usage statistics, and serves reports |
| justniffer | Network TCP packet sniffer with reliable TCP flow rebuilding |
| tcpflow | TCP/IP packet demultiplexer |
| tcpdump | Powerful and hugely respected command-line packet analyzer |
| sniffglue | Packet sniffer written in Rust |
| sniffer | Alternative network traffic sniffer |
| RustNet | Terminal monitor for connections and bandwidth |
| Malcolm | Traffic analysis suite for capture, hunting and forensics |
| dsniff | Collection of tools for network auditing and penetration testing |
| ngrep | grep applied to the network layer |
| Network Monitor | Rreal-time network connection monitoring tool |
| sniffit | CORBA based sniffer system with ncurses interactive mode |
| Jomon | Network forensics and sniffer tool |
Read our verdict in the software roundup.
 LinuxLinks helps you discover the best free and open source software for Linux. Explore our extensive collection of recommended applications, including alternatives to popular proprietary software. We also publish software reviews, Linux tutorials, hardware reviews, free programming books and articles covering the wider open source community. Browse our Linux resources to discover more. Know a useful free and open source Linux application we haven't covered? Suggest a program for inclusion. Has your software been featured on LinuxLinks? Display one of our Featured on LinuxLinks badges on your website or GitHub README. |
Please read our Comment Policy before commenting.