
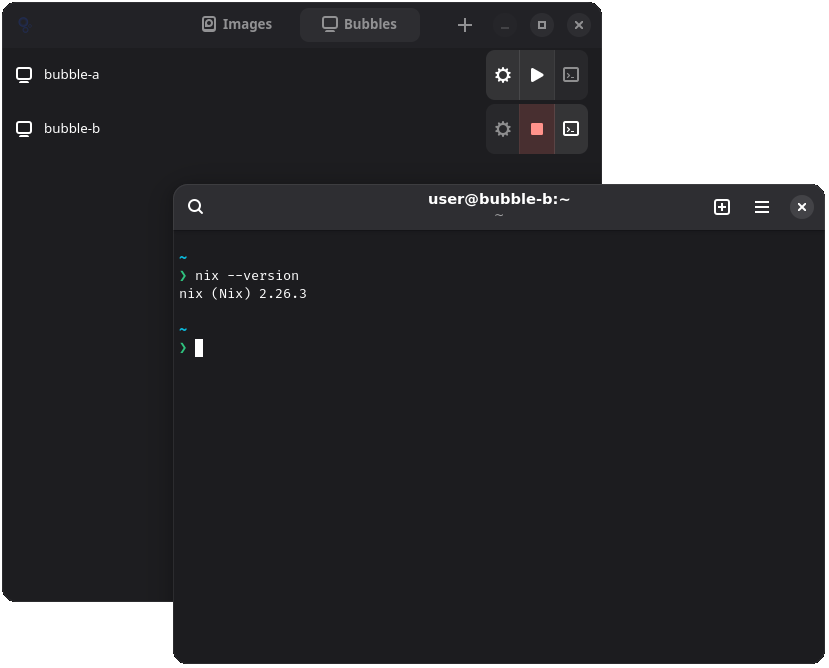
Bubbles creates lightweight Linux working environments that combine much of the flexibility of a container with a stronger virtual machine isolation boundary. Each Bubble provides a real Debian installation which can be kept for long-term work or discarded after short experiments.
The software uses KVM and crosvm for isolation while integrating graphical applications with the host Wayland compositor. Networking is designed to be transparent, helping applications inside the environment behave naturally without requiring the sort of manual network configuration associated with conventional virtual machines.
Bubbles runs as an unprivileged Flatpak and is particularly interesting on immutable and atomic distributions. Each environment includes Nix for reproducible package management, but Debian’s apt and other package managers can also be used. Containers can be run inside a Bubble, making the software useful for development, testing and keeping unrelated working environments separated.
This is free and open source software.
Key Features
- Create persistent or disposable Debian working environments.
- Uses KVM and crosvm to provide a strong isolation boundary.
- Integrates application windows with the host Wayland compositor.
- Provides transparent networking between the environment and host.
- Runs as a sandboxed, least-privilege Flatpak.
- Includes Nix for reproducible package management.
- Supports Debian’s apt and alternative package managers.
- Allows containers and development environments to run inside a Bubble.
Website: github.com/gonicus/bubbles
Support:
Developer: GONICUS GmbH
License: MIT License
Bubbles is written in Rust. Learn Rust with our recommended free books and free tutorials.
Related Software
| Application Sandboxing Tools | |
|---|---|
| Firejail | Linux SUID sandbox for restricting application access |
| bubblewrap | Low-level tool for building unprivileged sandboxes |
| NsJail | Process isolation tool using namespaces, cgroups, and seccomp filters |
| Isolate | Secure execution environment for running untrusted programs with limits |
| Syd | Application sandbox providing configurable filesystem and syscall isolation |
| Hakoniwa | Process isolation tool built around Linux namespaces and security facilities |
Read our verdict in the software roundup.
 Explore our carefully curated directory of recommended free and open source software, covering every major software category. The directory forms part of our extensive collection of articles for Linux enthusiasts. It includes hundreds of detailed reviews, together with free and open source alternatives to proprietary software from companies such as Google, Microsoft, Apple, Adobe, IBM, Cisco, Oracle, and Autodesk. LinuxLinks also covers interesting projects worth exploring, Linux-compatible hardware, free programming books and tutorials, and much more. Know a useful free and open source Linux application that we haven’t covered? Tell us about it using our submission form. |
Please read our Comment Policy before commenting.