
Logstash is an open source tool for managing events and logs.
You can use it to collect logs, parse them, and store them for later use (like, for searching).
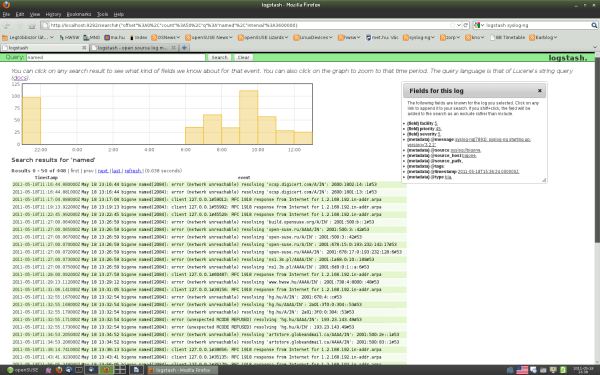
Logstash comes with a web interface for searching and drilling into all of your logs.
Key Features
- Three main components to a logstash agent – Input/Filters/Output
- Input:
- Files.
- stdin.
- email (cron jobs).
- syslog servers – take syslog messages over the network.
- Flume.
- Message brokers – (AMQP, STOMP, Beanstalk).
- Twitter stream API.
- HTTP, TCP socket.
- Supports wildcards.
- Filters which give structure to the logs:
- Timestamp parsing.
- Date parsing (needed because everyone invents their own time format).
- Grep (drops things that do/dont match).
- grok – compact syntax for writing a pattern matching machine.
- grok discovery – start with a sample from your logs. Grok’s discovery will try to generate a pattern that matches it.
- Drop events.
- Parse fields.
- Anonymize.
- Multiline – join related log lines in a single event.
- Output to:
- ElasticSearch – scalable indexing for logs, uses Lucene (full text search system as backend).
- Message Brokers – AMQP, STOMP, Beanstalk – take data from remote nodes and ship them over to a message system. This allows you to build a scalable message transportation by sending events from your servers and devices into a message system and have them farmed out to other logstash receivers using the same message system as an input.
- Graylog2 (GELF) – ship events to a graylog2 server.
- MongoDB – write to events to.
- Nagios – trigger Nagios alerts from events.
- WebSockets – lets you stream events in real-time to your browser.
- TCP.
- syslog.
- Chain agents together on different systems to create a networked pipeline for inputting, filtering, and outputting events.
- User interface:
- Search by field or full text.
- Graph results over time.
- See search results and page through them.
- Drill into events.
- Add your own input, output, or filter plugins to logstash.
Website: www.elastic.co/products/logstash
Support: Reference, GitHub Code Repository
Developer: Elasticsearch B.V
License: Apache 2.0
Logstash is written in Ruby and Java. Learn Ruby with our recommended free books and free tutorials. Learn Java with our recommended free books and free tutorials.
Related Software
| Log Analyzers | |
|---|---|
| Kibana | Browser based interface for logstash and ElasticSearch |
| logstash | Log processing, search, and analytics |
| OpenObserve | Cloud-native observability platform |
| GoAccess | Real-time web log analyzer and interactive viewer |
| Fluentd | Data collector for unified logging layer |
| Loki | Horizontally-scalable, highly-available, multi-tenant log aggregation system |
| Graylog2 | Log management solution implementation storing logs in ElasticSearch |
| Graphite | Enterprise scalable realtime graphing |
| SigNoz | Monitor your applications and troubleshoot problems |
| Apache Flume | Delivers data from applications to Apache Hadoop's HDFS |
| OpenTSDB | Scalable, distributed Time Series Database |
| VictoriaLogs | High-performance log database designed to ingest, store, and query log data |
| Scribe | Server for aggregating log data that is streamed in real time from clients |
| LogoRRR | Cross-platform log analysis tool |
| Chukwa | Hadoop sub-project devoted to large-scale log collection and analysis |
Read our verdict in the software roundup.
 LinuxLinks helps you discover the best free and open source software for Linux. Explore our extensive collection of recommended applications, including alternatives to popular proprietary software. We also publish software reviews, Linux tutorials, hardware reviews, free programming books and articles covering the wider open source community. Browse our Linux resources to discover more. Know a useful free and open source Linux application we haven't covered? Suggest a program for inclusion. Has your software been featured on LinuxLinks? Display one of our Featured on LinuxLinks badges on your website or GitHub README. |
Please read our Comment Policy before commenting.